Kernel Resource Eviction (OOMKilled)
Detection pattern:
OOMKilled + Exit 137
This is a deterministic Kubernetes incident diagnostics engine powered by the PBRCIM (Pattern-Based Root Cause Isolation Model) framework. It analyzes cluster logs to isolate workload, networking, scheduling, storage, runtime, and infrastructure failures in under 10ms. It is a secure, offline lightweight engine that requires zero APIs and zero cloud dependency.
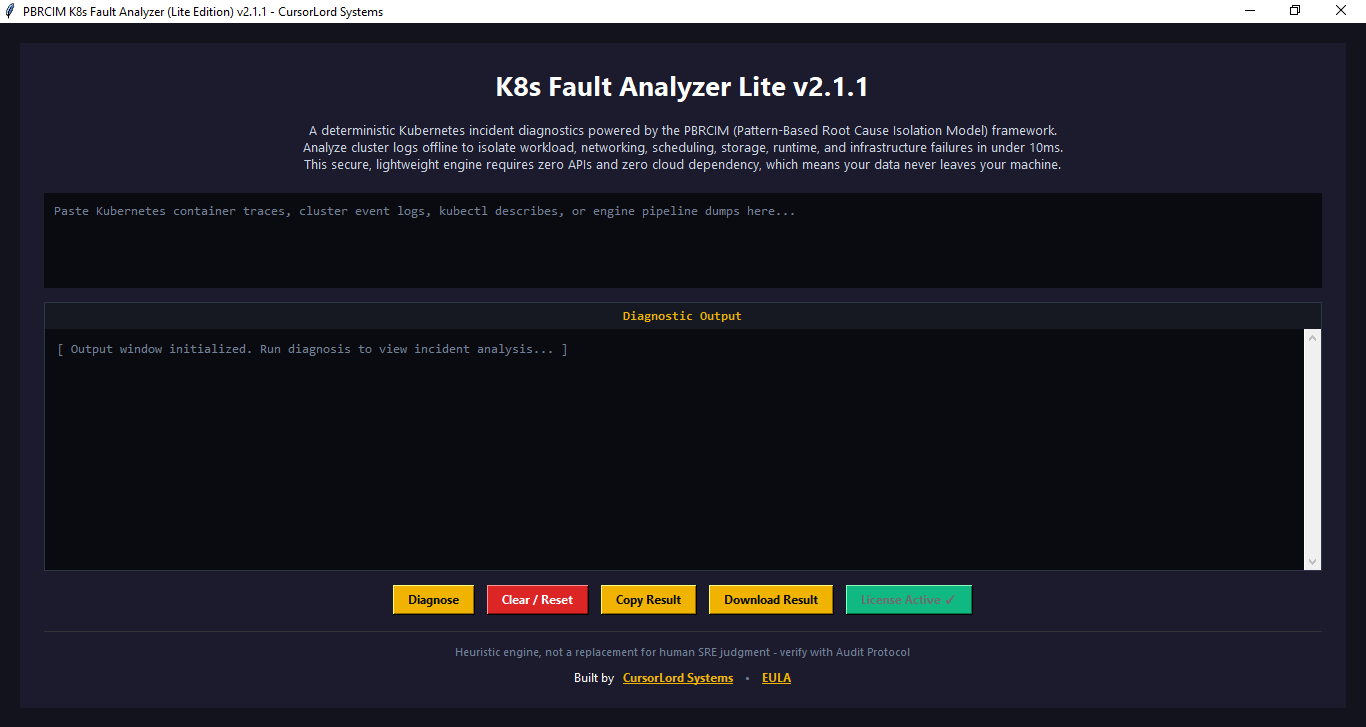
The K8s Fault Analyzer (Lite Edition) v2.1.1 is an offline, air-gapped diagnostic utility engineered as a proprietary internal asset. Rather than relying on cloud LLM APIs or generic scripts, we deploy this deterministic parser to power CursorLord Systems Managed K8s Incident Response, delivering sub-second root-cause post-mortems for production outages.
This elite tool covers 10 focused fault vectors and diagnoses around 80% of the daily crash scenarios SREs actually face in production (Memory/OOM, Registry/Auth, mTLS, Storage Mounts, RBAC, Admission Webhooks, Node Pressure, Probe Drops, etc.)
Detection pattern:
OOMKilled + Exit 137
Detection pattern:
admission webhook.*denied | failed calling webhook
Detection pattern:
ImagePullBackOff | ErrImagePull + Failed to pull image | unauthorized
Detection pattern:
FailedScheduling + Insufficient cpu | memory | 0/.* nodes available
Detection pattern:
MountVolume.*failed | configmap.*not found | secret.*not found
Detection pattern:
forbidden:.*cannot | serviceaccount.*cannot list | create | RBAC
Detection pattern:
persistentvolumeclaim.*Pending | FailedAttachVolume | no persistent volumes available
Detection pattern:
Node.*NotReady | Kubelet.*PLEG is not healthy | NodeReady.*False
Detection pattern:
DiskPressure | Evicted.*ephemeral-storage | no space left on device
Detection pattern:
x509: certificate has expired | tls:.*handshake failure | certificate.*expired
The clean, ready-to-copy, post-mortem report from the tool includes:
Image Registry Security & Authentication Divergence (401/403)
Pod Image Node Registry Namespace
kubectl describe
crictl pull
kubectl create secret
I build deterministic diagnostic tools and help teams investigate complex production incidents. My focus is on structured log analysis, root-cause isolation, and deep-systems troubleshooting.
Available for debugging engagements, incident analysis and custom diagnostic tooling.
How to share your logs safely
Please strip out sensitive details before sending your log snippet. Replace private internal URLs, API tokens, passwords, public IP addresses, customer data, or credentials with simple dummy values (e.g., postgres://user:XXXXX@internal-db:5432/db or ip-10-0-x-x). Standard Kubernetes event names, pod names, and stack traces can remain intact.